# Cybersecurity issue: CWE-798 hard-coded authentication in web client side
**URL:** https://community.glideapps.com/t/cybersecurity-issue-cwe-798-hard-coded-authentication-in-web-client-side/78702
**Category:** Report a Bug
**Tags:** security
**Created:** [December 20, 2024, 4:48am UTC](https://community.glideapps.com/t/cybersecurity-issue-cwe-798-hard-coded-authentication-in-web-client-side/78702 "2024-12-20T04:48:54Z")
**Posts on this page:** 7
**Page:** 1
### Author:  [@Samuel.Chou.OM](https://community.glideapps.com/u/Samuel.Chou.OM)
#### Post date: [December 20, 2024, 4:48am UTC](https://community.glideapps.com/t/cybersecurity-issue-cwe-798-hard-coded-authentication-in-web-client-side/78702/1 "2024-12-20T04:48:54Z")
**Team ID:**
`https://go.glideapps.com/o/lxYiTW2xZd5JdolIXarV/`
**App ID:**
`https://go.glideapps.com/app/TusQVIs3ZvE7aC2eR6ws/layout`
**Description**
As our client requested, we ran an source code security analysis report, targeting the source code from web-client side.
The result shows that there’s a risk called “Credential Management: Hardcoded API Credentials”, type “CWE-798”, which is leveled as Critical risk.
I wonder if the team could fix it soon? As client asking that if this should be worried about.
**How to replicate**
1. Open any of your Glide App web-client page.
2. Navigate to the Sources. For example, in Google Chrome, open DevTools \> Sources.
3. Navigate to the code of `sw-prod-v4.js` \> `your-app-name.glide.page` \> `static/js` \> `sw-common-alotoftokens.js`
4. Search keywords in the code, ex. `apiKey:` `appId`
You will find some keys / auth tokens are hard-coded in that script, like this:

I took a quick look to other website services like WordPress, wix, Google, Facebook, etc. It seems that the hard-coded authentication does not exist in their web service.
---
### Author:  [@MaximeBaker](https://community.glideapps.com/u/MaximeBaker)
#### Post date: [December 20, 2024, 11:29am UTC](https://community.glideapps.com/t/cybersecurity-issue-cwe-798-hard-coded-authentication-in-web-client-side/78702/2 "2024-12-20T11:29:20Z")
The API key is probably an ANON key.
@NoCodeAndy Am I right?
---
### Author:  [@Samuel.Chou.OM](https://community.glideapps.com/u/Samuel.Chou.OM)
#### Post date: [April 15, 2025, 3:10am UTC](https://community.glideapps.com/t/cybersecurity-issue-cwe-798-hard-coded-authentication-in-web-client-side/78702/3 "2025-04-15T03:10:39Z")
Hello, got any updates this one?
---
### Author:  [@MaximeBaker](https://community.glideapps.com/u/MaximeBaker)
#### Post date: [April 15, 2025, 10:40am UTC](https://community.glideapps.com/t/cybersecurity-issue-cwe-798-hard-coded-authentication-in-web-client-side/78702/4 "2025-04-15T10:40:44Z")
@comm_support_agent
---
### Author:  [@Samuel.Chou.OM](https://community.glideapps.com/u/Samuel.Chou.OM)
#### Post date: [June 11, 2025, 5:28am UTC](https://community.glideapps.com/t/cybersecurity-issue-cwe-798-hard-coded-authentication-in-web-client-side/78702/5 "2025-06-11T05:28:37Z")
Hello, any updates on this?
---
### Author:  [@Jeff\_Hager](https://community.glideapps.com/u/Jeff_Hager)
#### Post date: [June 11, 2025, 12:09pm UTC](https://community.glideapps.com/t/cybersecurity-issue-cwe-798-hard-coded-authentication-in-web-client-side/78702/6 "2025-06-11T12:09:07Z")
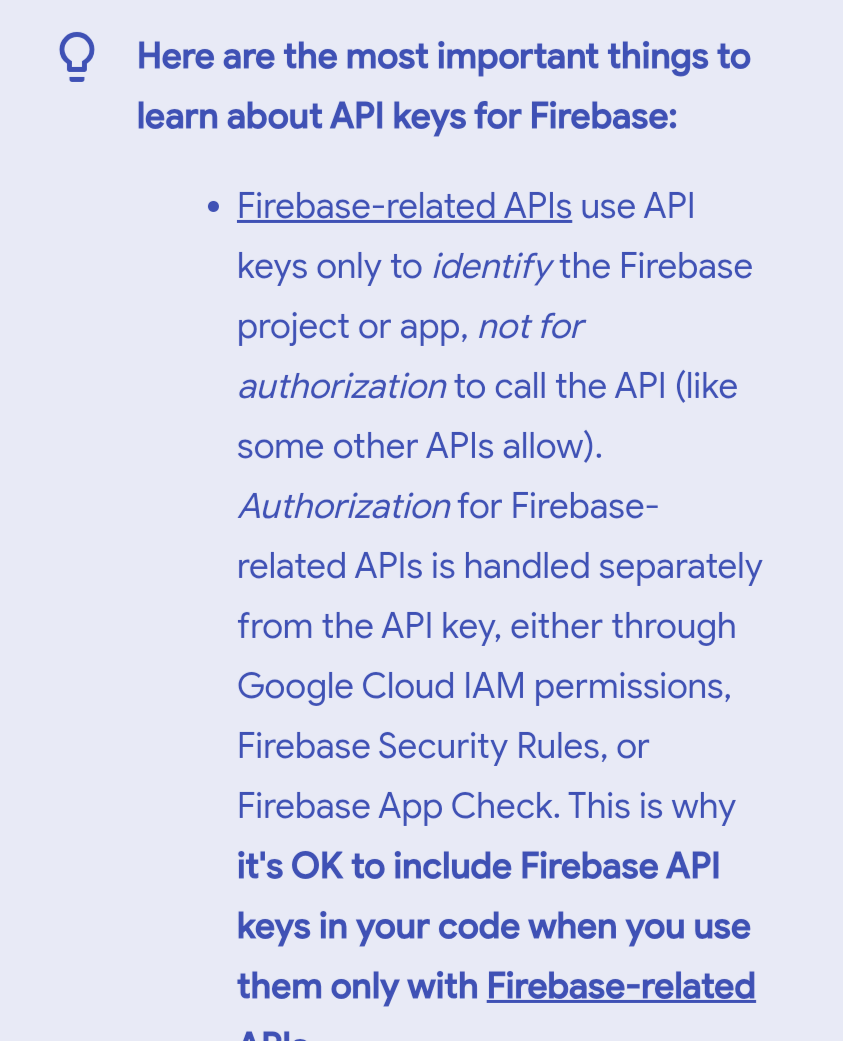
> **[Learn about using and managing API keys for Firebase | Firebase...](https://firebase.google.com/docs/projects/api-keys?utm_source=chatgpt.com#api-keys-for-firebase-are-different)**
> **[Reddit - The heart of the internet](https://www.reddit.com/r/Firebase/comments/12xxl4d/how_do_i_hide_my_firebaseconfig/?utm_source=chatgpt.com)**
[https://stackoverflow.com/questions/37482366/is-it-safe-to-expose-firebase-apikey-to-the-public](https://stackoverflow.com/questions/37482366/is-it-safe-to-expose-firebase-apikey-to-the-public)
[https://stackoverflow.com/questions/74365032/is-exposing-the-api-key-from-firebase-at-url-firebase-messaging-sw-js-a-security/74368266?utm\_source=chatgpt.com](https://stackoverflow.com/questions/74365032/is-exposing-the-api-key-from-firebase-at-url-firebase-messaging-sw-js-a-security/74368266?utm_source=chatgpt.com)
> **[Do you need to hide your Firebase API keys in your ionic apps?](https://jorgevergara.co/blog/hide-firebase-api/?utm_source=chatgpt.com)**
>
> Learn if and how you need to secure your firebase api keys
---
### Author:  [@system](https://community.glideapps.com/u/system)
#### Post date: [August 18, 2025, 7:08am UTC](https://community.glideapps.com/t/cybersecurity-issue-cwe-798-hard-coded-authentication-in-web-client-side/78702/7 "2025-08-18T07:08:19Z")
This topic was automatically closed 7 days after the last reply. New replies are no longer allowed.